by
https://i.ibb.co/K6xSvDk/pt1.jpg
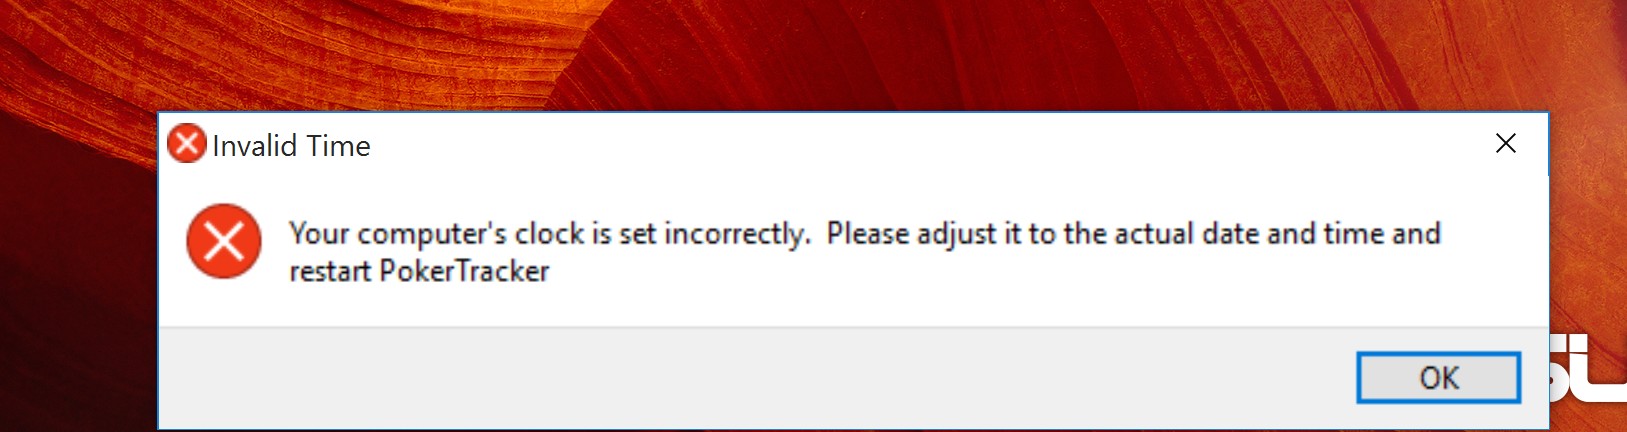
...I had to upgrade PT4 (v4.15.20), but I get this in return: VBA32: BScope.TrojanPSW.Phpw
https://www.virustotal.com/gui/file/0616f2b5fb98109a184905c87c61946975143e61287046f9a69c8a33be89050f/detection
PT-Install-v4.15.20.exe
https://www.f-secure.com/v-descs/trojan-psw_w32_papras_dc.shtml
Trojan-PSW.Win32.Papras.DC steals login credentials and other sensitive information on the compromised system. It also drops and uses a rootkit driver to hide itself. The rootkit driver is detected as Rootkit.Win32.Agent.SZ.
I demand an explanation.